Multi-layered cloud firewall & access security
Protect virtual infrastructure with cloud security group rules, hypervisor firewall plans, ConfigServer Security & Firewall (CSF) brute-force protection, Two-Factor Authentication (2FA), and granular Role-Based Access Control (ACL) permissions.
Virtualization security groups & host firewall filtering
Defend virtual machines and node interfaces with stateful firewall policies, anti-DDoS rules, and multi-factor authentication.
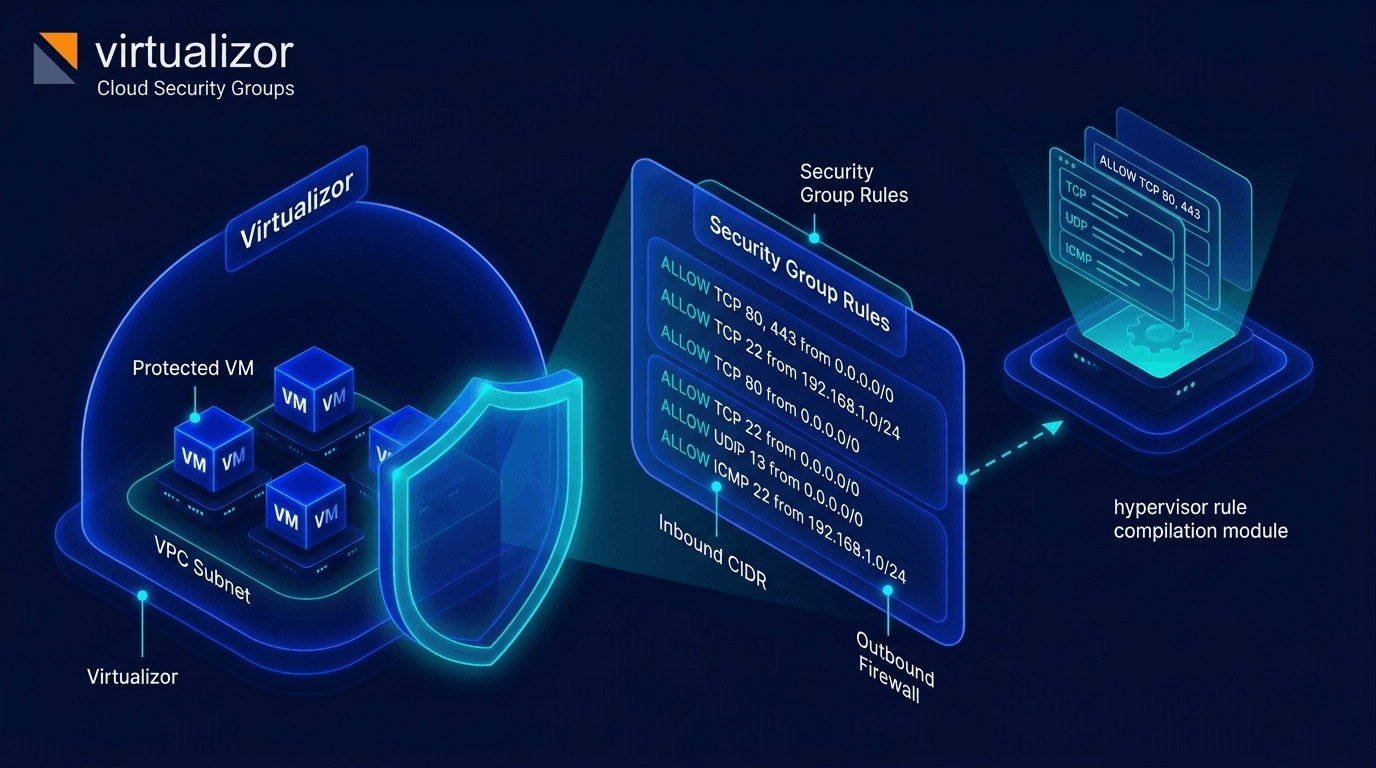
- Stateful Inbound & Outbound Security Group rules with CIDR IP filtering
- Node-level iptables & nftables firewall plans with customizable default policies
- Integrated CSF control panel for automatic port scan & brute-force IP blocking
- TOTP 2FA (Google Authenticator) & IP-whitelisted API access credentials
Four layers of enterprise cloud protection
Configure security groups, node firewall rules, brute-force shields, and authentication controls.
1. Define Security Groups
Create reusable Security Group profiles with custom inbound and outbound port rules, protocol types, and CIDR targets.
2. Attach to VMs & VPCs
Assign security groups to individual guest VMs or entire VPC subnets for automated hypervisor-level packet filtering.
3. Enable CSF Shield
Activate CSF firewall integration on master and slave nodes to detect and block malicious login attempts automatically.
4. Enforce 2FA & ACLs
Require Google Authenticator 2FA for account logins and restrict operator capabilities using granular Role-Based Access Control.
Enterprise threat protection & access control
Full control over cloud security groups, node firewalls, CSF integration, and 2FA authentication.
Cloud Security Groups
Build reusable stateful security group rule sets. Filter traffic by protocol (TCP, UDP, ICMP), port ranges (e.g. 80, 443, 22), and source or destination CIDR IP blocks.
- Inbound & Outbound CIDR rule mapping
- Attach to individual VMs or VPC subnets
- Real-time hypervisor iptables rule compilation
CSF & node firewall plans
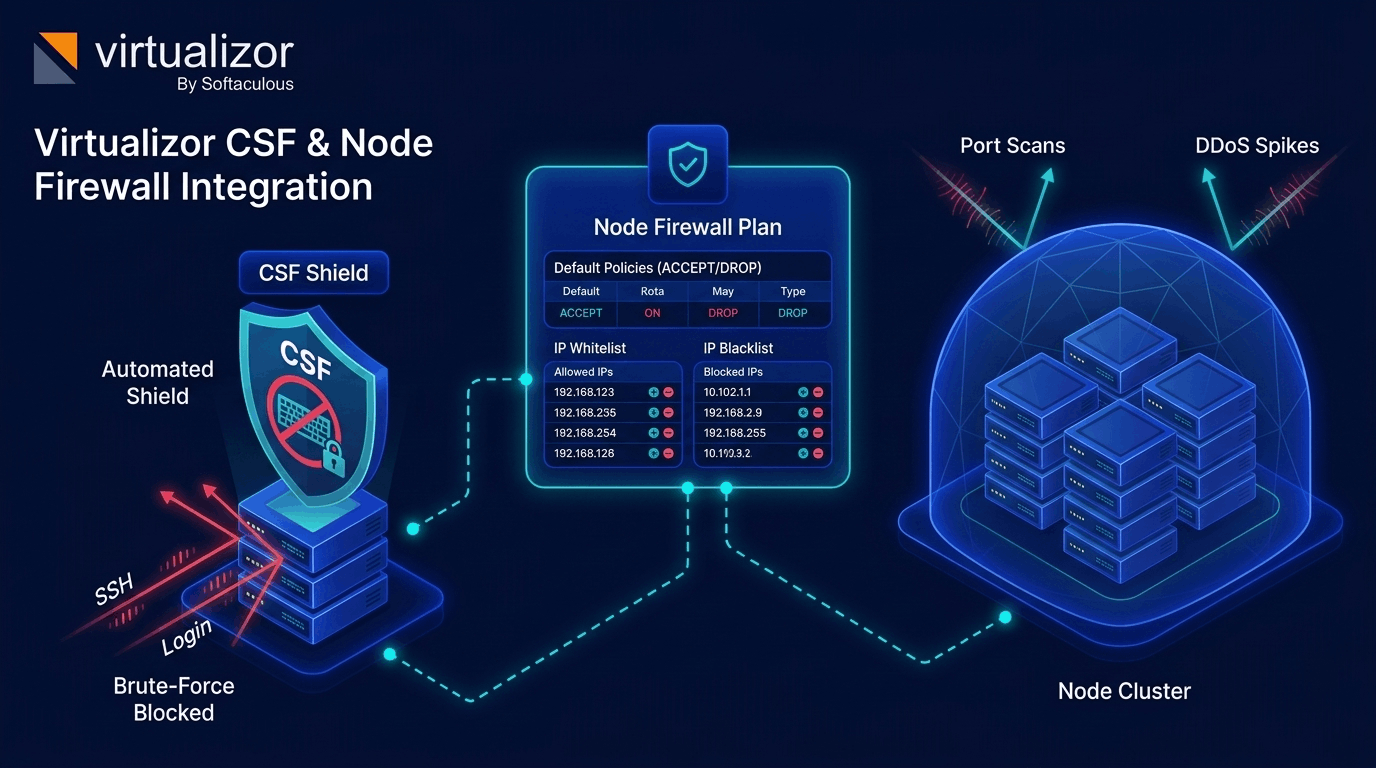
Manage node firewall plans and integrate ConfigServer Security & Firewall (CSF). Automatically block brute-force SSH/panel logins, port scans, and DDoS traffic spikes.
- CSF brute-force detection & automatic IP bans
- Node-level default ACCEPT / DROP policies
- IP whitelisting & blacklisting management
2FA authentication & ACLs
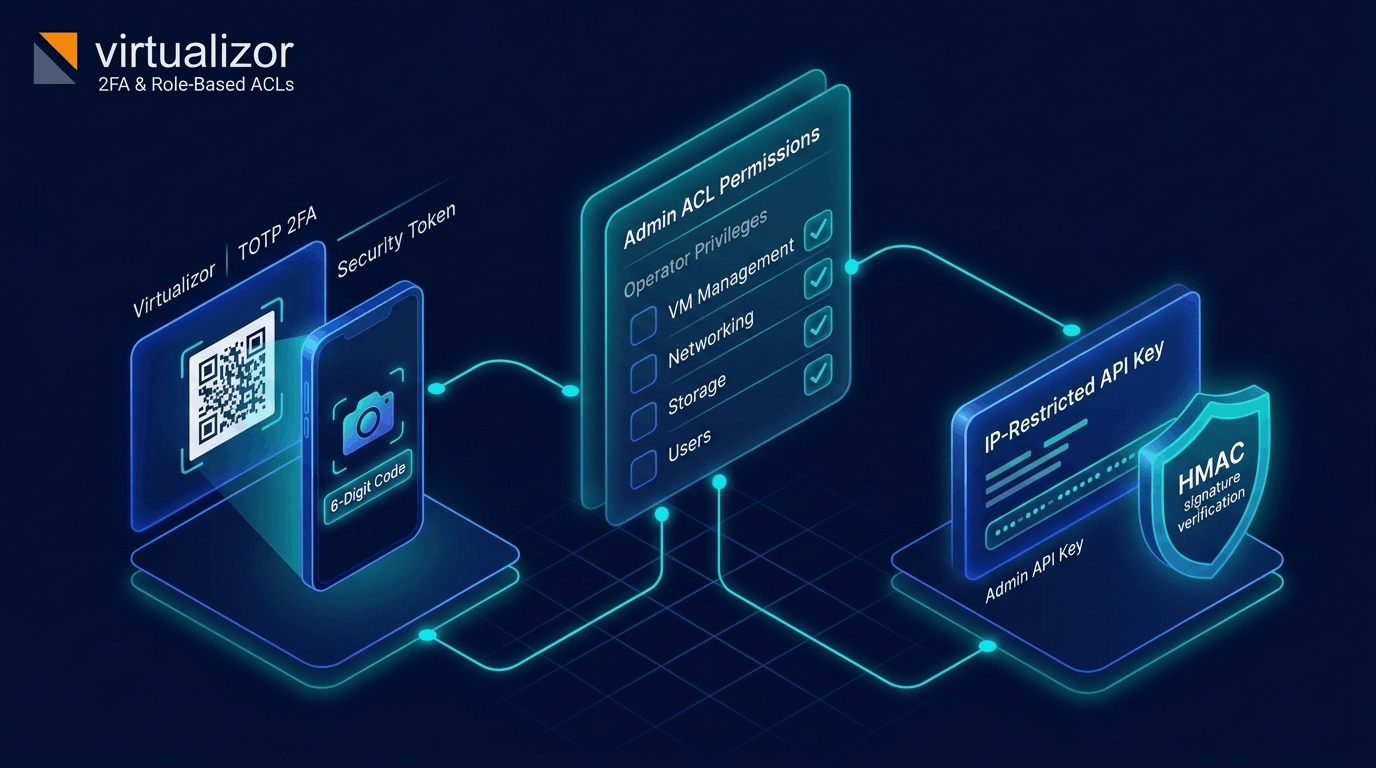
Enforce TOTP Two-Factor Authentication (Google Authenticator / Authy) for admin operators and endusers. Define granular ACL permissions and IP-restricted API credentials.
- TOTP Two-Factor Auth (2FA) for Admin & Clients
- Granular Role-Based Access Control (ACL) flags
- IP-restricted API Key pairs & access tokens
Firewall & Security specifications
Technical specifications of Virtualizor's Security Groups, CSF integration, and 2FA authentication.
| Status | Surface / Feature | Capability & Technical Detail |
|---|---|---|
| Security Groups | Inbound & Outbound stateful rule engine, protocol filtering (TCP, UDP, ICMP), custom port ranges, and CIDR targets. | |
| Host & VM Firewall | Node-level firewall policies and per-VM hypervisor iptables and ebtables filtering with default DROP or ACCEPT rules. | |
| CSF & LFD Shield | ConfigServer Security & Firewall integration with automated SSH and panel brute-force IP bans, port scan protection, and LFD daemon. | |
| Multi-Factor Auth | TOTP Two-Factor Authentication for Admin and Enduser panel logins, backup recovery codes, and QR code provisioning. | |
| Role-Based ACLs | Granular Admin role permissions and Enduser self-service access limits across VM lifecycle, network, and storage. | |
| API Credentials | IP-restricted API Key and Secret pairs, HMAC request signature validation, and real-time API invocation audit logging. | |
| Audit Logs & Sessions | Active user session tracking and remote termination, IP access audit logs, and complete administrator activity trails. | |
| SSL & Abuse Security | Automated Let's Encrypt SSL issuance and auto-renewal, customer KYC identity verification, and CVE vulnerability scanners. |
Complete production cloud security
Combine Cloud Security Groups with software-defined VPC subnets and Whitelabel reseller portals.
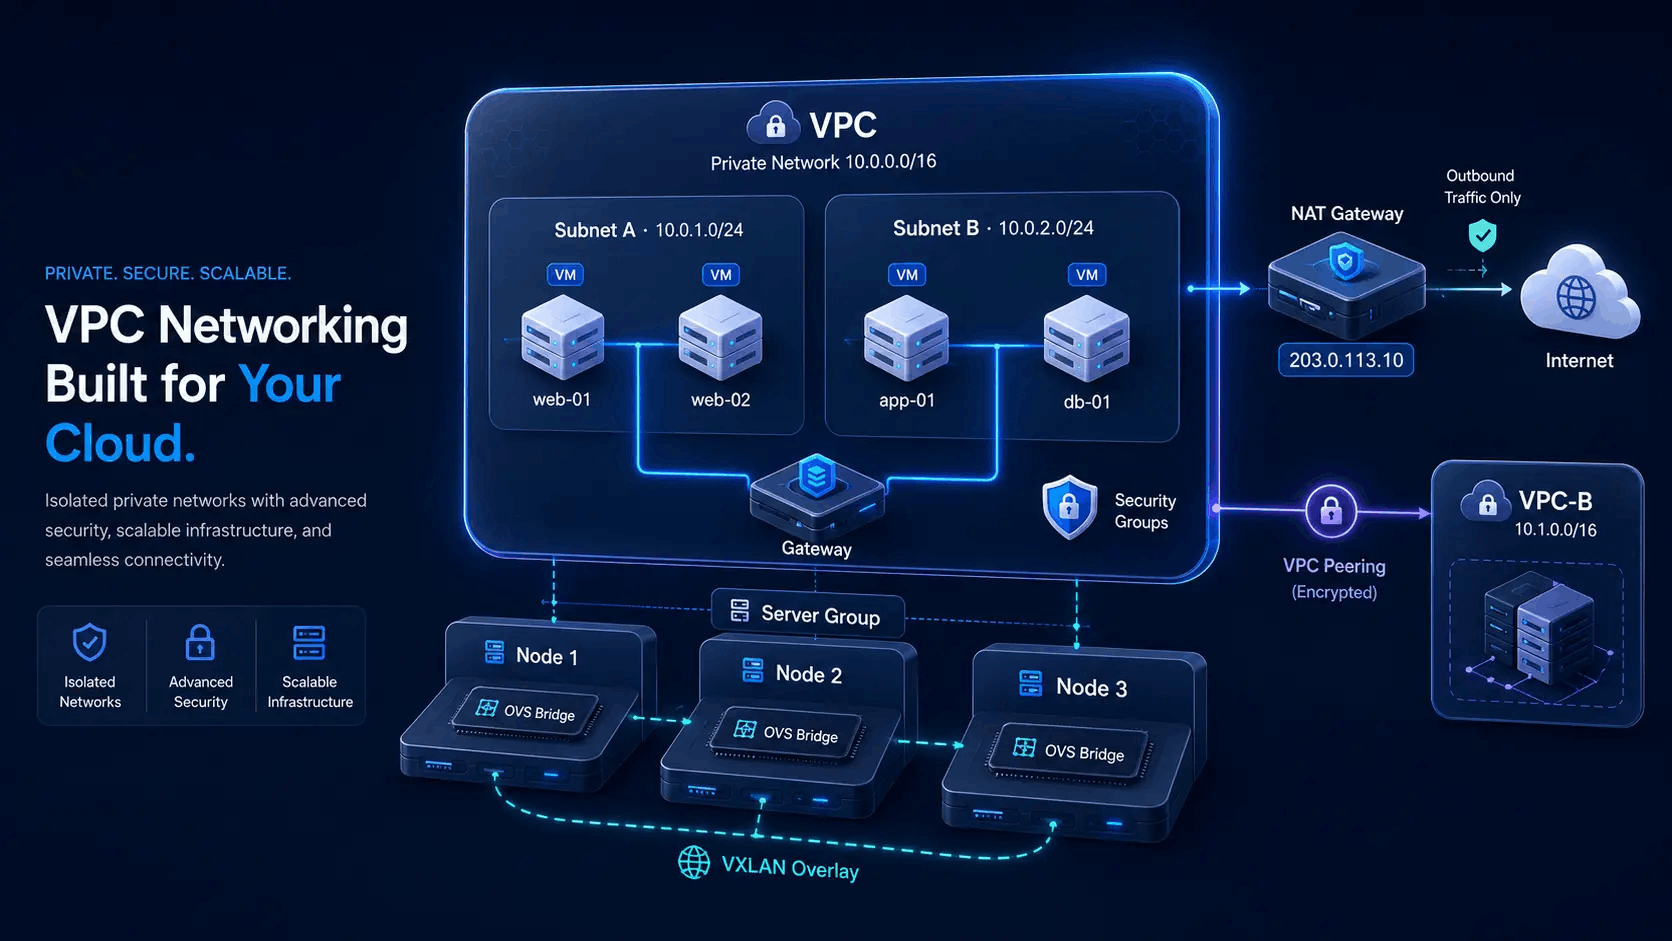
VPC Network Isolation & NAT
Deploy private VPC networks with isolated subnets, floating public IPs, NAT gateways, and security groups.
Explore VPC NetworkingWhitelabel & Reseller Security
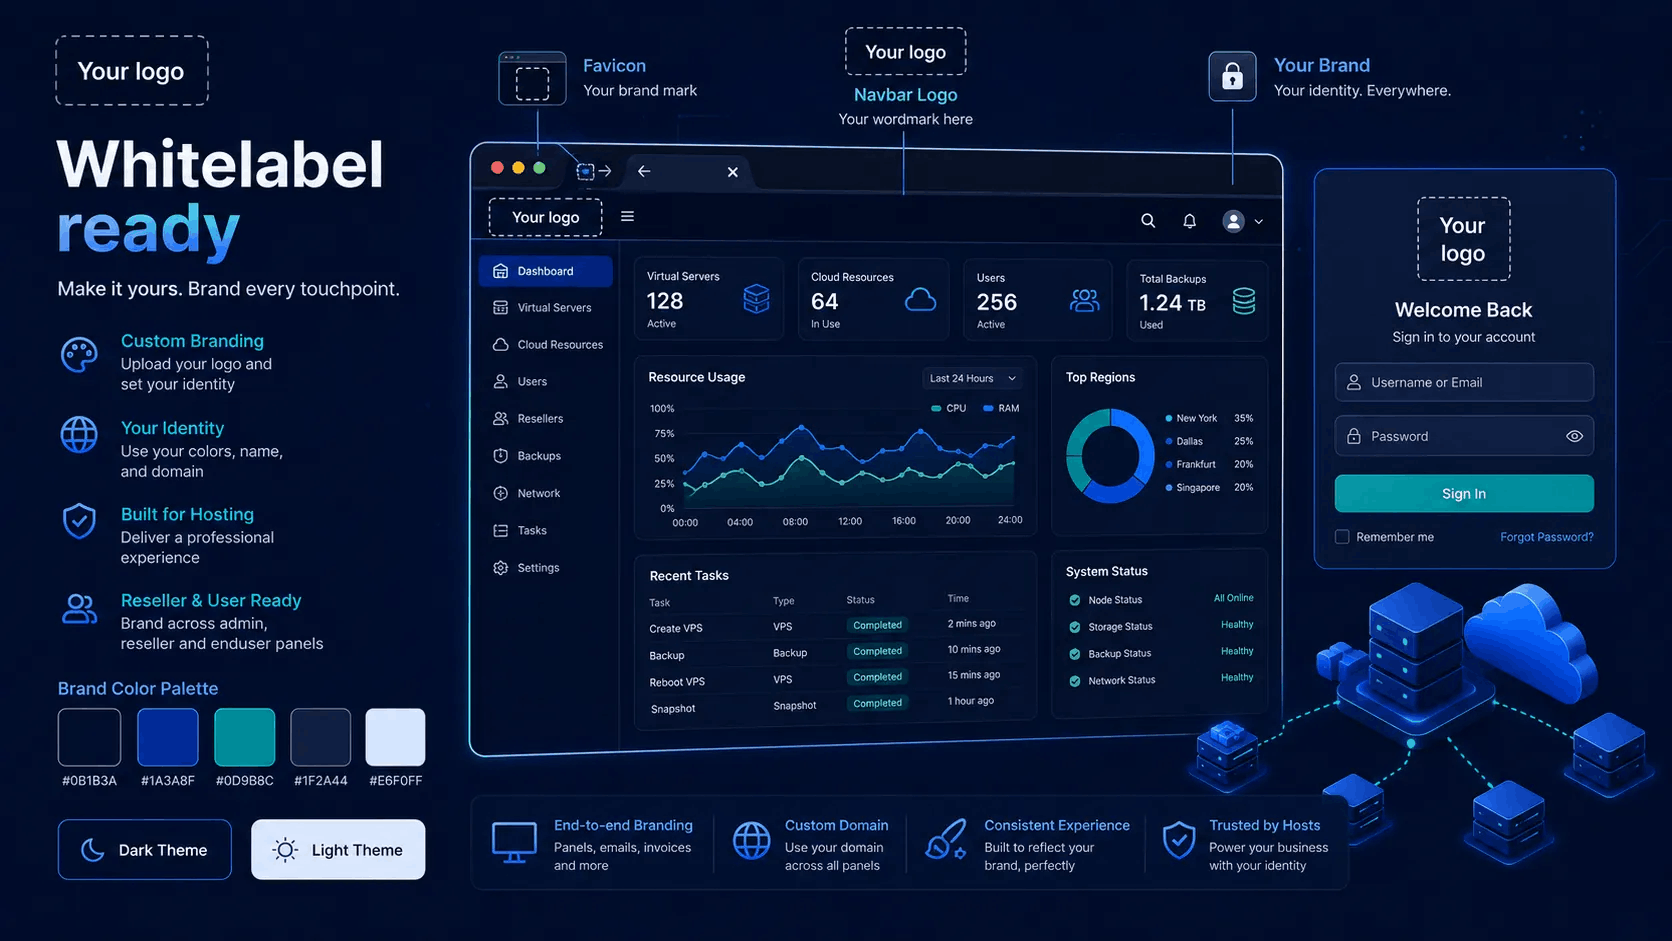
Apply 2FA authentication and granular ACL permission limits across branded reseller cloud portals.
Explore WhitelabelAdmin security policy, enduser rule management
Role-based control for security group policies, CSF firewall rules, and 2FA enforcement.
System Administrators
- Configure node-level firewall plans & CSF brute-force thresholds
- Create global Security Group templates & CIDR rule policies
- Require TOTP 2FA for administrator & reseller account logins
- Manage operator ACL permissions & inspect API security audit logs
Endusers & Cloud Clients
- Create custom Security Groups for virtual machines & VPC subnets
- Define inbound and outbound TCP, UDP & ICMP port rules
- Enable TOTP Two-Factor Auth (Google Authenticator) on client accounts
- Generate IP-restricted API Key pairs for personal automation